Loading...
About Us

Welcome to Sina Academy

Welcome to a place where dreams take flight and knowledge knows no bounds. Embrace the journey, dear students.

Step into the halls of wisdom, where each welcome is a promise of growth and every challenge is an opportunity to shine.

Skilled Instructors

Online Classes

International Certificate

Join Our Team

Become an Instructor

Share your knowledge and expertise with students worldwide. Join our community of educators and make a difference in online learning.

Flexible Teaching

Global Reach

Competitive Compensation

Professional Development

Apply Now
News & Events

Latest Updates

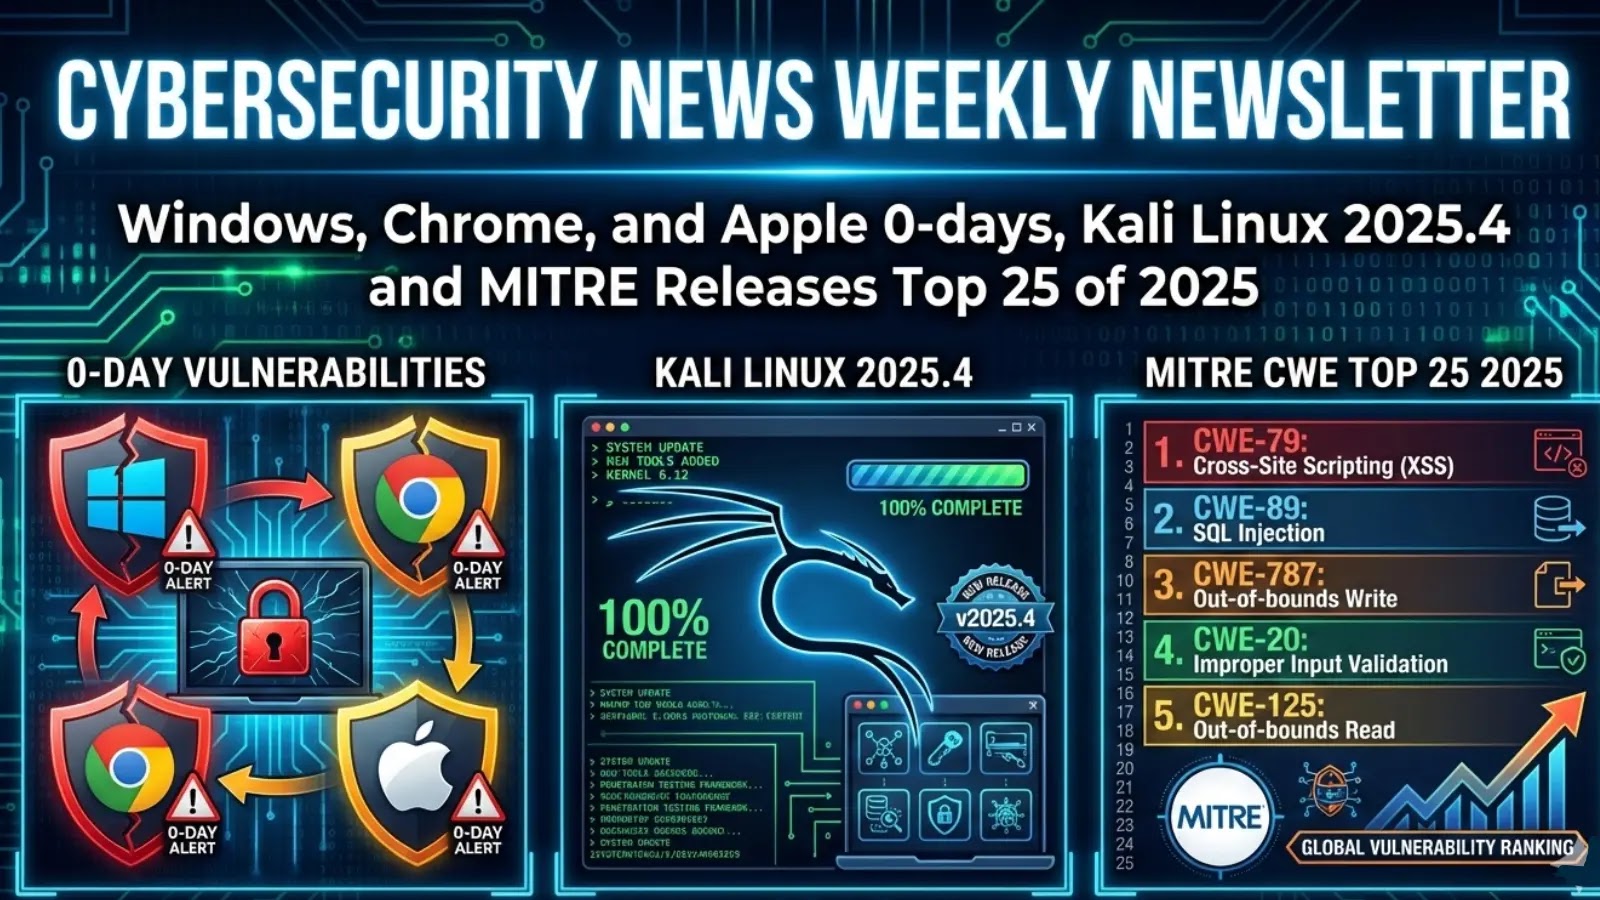
Cybersecurity News Weekly Newsletter – Windows, Chrome, and Apple 0-days, Kali Linux 2025.4, and MITRE Top 25
News Dec 24, 2025

As 2025 nears its close, the cybersecurity landscape shows no signs of slowing down. This week’s developments highlight how rapidly the threat environment continues to evolve with major zero-day vulnerabilities targeting Windows, Chrome, and Apple devices, each actively exploited in the wild. These high-risk flaws underline the continued importance of swift patching, layered defense, and continuous threat monitoring across enterprise ecosystems. Meanwhile, offensive security professionals received a major update as Kali Linux 2025.4 rolled out with new tools, kernel upgrades, and enhanced cloud integration, reinforcing its position as a cornerstone for penetration testing and digital forensics in both research and operational security settings. On the defensive front, MITRE released its annual Top 25 Most Dangerous Software Weaknesses of 2025, spotlighting recurring coding errors that adversaries frequently weaponize. From inadequate input validation to risky resource management, the list serves as a vital reminder that secure coding is still the first line of defense against complex exploitation techniques and chained attack vectors. Across the board, this week reflects a convergence of aggressive exploitation activity and heightened community response. Organizations are urged to prioritize visibility, validate software supply chains, and stay aligned with evolving security frameworks. Whether patching systems affected by 0-days, assessing exposure through MITRE’s latest findings, or adopting the latest features of Kali Linux, the takeaway is clear — cyber resilience depends on agility, awareness, and readiness. Stay ahead of the threat curve with this week’s highlights, advisories, and actionable updates across infrastructure, endpoint, and application security domains.

Happy Shab-e-yalda!
Happy Shab-e-yalda!
Event Dec 24, 2025

Tonight, the longest night of the year, is an opportunity to be together and celebrate love and friendship. Let's fill this special night with the light of our hearts and welcome a new season. Every pomegranate seed and watermelon slice symbolizes the wonders of life and hope for brighter days ahead. Let's revive sweet memories with stories and poems of Hafez, and plant joy in our hearts. May our hearts be filled with hope and happiness at dawn on Yalda, and may the new year be full of blessings and fulfilled wishes for all of you. May your Yalda be full of light and joy!

A Major Step for Global Tech Education
News Dec 19, 2025

SINA Academy, the premier online college dedicated to advanced technology and computer science studies, proudly announces its official membership into the prestigious Global School Alliance (GSA). This significant achievement marks SINA Academy's commitment to adhering to international standards of educational quality and expanding its influence across the global academic landscape. The Global School Alliance is an influential international network that connects educational institutions dedicated to excellence, collaboration, and improving student outcomes worldwide. Elevating Global Standards The GSA membership provides SINA Academy with unparalleled access to international educational leaders, resources, and continuous professional development, ensuring that SINA's curriculum remains on the cutting edge of global technological demands. “Joining the Global School Alliance is a key strategic milestone for SINA Academy,” said [Name and Title of SINA Academy Leader, e.g., CEO/Director of Academics]. “It is a public commitment that our rigorous, project-based programs—from Cybersecurity to Artificial Intelligence—are benchmarked against the highest international standards. This affiliation directly enhances the global recognition and value of every certificate and qualification our students earn.” Benefits for SINA Academy Students For current and future SINA Academy students, this membership translates directly into an enhanced educational experience and increased career opportunities: Global Recognition: Affiliation with the GSA reinforces the credibility of SINA Academy’s certifications, making graduates more competitive in international job markets. Best Practices in Pedagogy: SINA Academy will leverage GSA partnerships to continuously refine its online learning models and integrate the latest and most effective teaching methodologies. Networking and Collaboration: Opportunities may arise for student and faculty participation in international collaborative projects and virtual exchange programs facilitated by the Alliance network. Commitment to the Future SINA Academy’s online model has always been focused on breaking down geographical barriers to high-quality education. The GSA membership solidifies this vision, positioning the academy as a trusted partner in preparing a globally ready, skilled technology workforce. We look forward to actively contributing to the Alliance's mission and furthering the cause of inclusive, high-quality digital education worldwide. SINA Academy offers specialized, fully online programs in Software Engineering, Cybersecurity, Data Science, Networking & Cloud Computing, Artificial Intelligence, and Web Engineering. Explore our programs and start your journey to a global tech career today.

Over 10,000 Docker Hub images found leaking credentials, auth keys
News Dec 15, 2025

More than 10,000 Docker Hub container images expose data that should be protected, including live credentials to production systems, CI/CD databases, or LLM model keys. The secrets impact a little over 100 organizations, among them are a Fortune 500 company and a major national bank. Docker Hub is the largest container registry where developers upload, host, share, and distribute ready-to-use Docker images that contain everything necessary to run an application. Developers typically use Docker images to streamline the entire software development and deployment lifecycle. However, as past studies have shown, carelessness in creating these images can result in exposing secrets that remain valid for extended periods. After scanning container images uploaded to Docker Hub in November, security researchers at threat intelligence company Flare found that 10,456 of them exposed one or more keys. The most frequent secrets were access tokens for various AI models (OpenAI, HuggingFace, Anthropic, Gemini, Groq). In total, the researchers found 4,000 such keys. When examining the scanned images, the researchers discovered that 42% of them exposed at least five sensitive values. "These multi-secret exposures represent critical risks, as they often provide full access to cloud environments, Git repositories, CI/CD systems, payment integrations, and other core infrastructure components," Flare notes in a report today. Analyzing 205 namespaces enabled the researchers to identify a total of 101 companies, mostly small and medium-sized businesses, with a few large enterprises being present in the dataset. Based on the analysis, most of the organizations with exposed secrets are in the software development sector, followed by entities in the market and industrial, and AI and intelligent systems. More than 10 finance and banking companies had their sensitive data exposed. According to the researchers, one of the most frequent errors observed was the use of .ENV files that developers use to store database credentials, cloud access keys, tokens, and various authentication data for a project. Additionally, they found hardcoded API tokens for AI services being hardcoded in Python application files, config.json files, YAML configs, GitHub tokens, and credentials for multiple internal environments. Some of the sensitive data was present in the manifest of Docker images, a file that provides details about the image. Many of the leaks appear to originate from the so-called 'shadow IT' accounts, which are Docker Hub accounts that fall outside of the stricter corporate monitoring mechanisms, such as those for personal use or belonging to contractors. Flare notes that roughly 25% of developers who accidentally exposed secrets on Docker Hub realized the mistake and removed the leaked secret from the container or manifest file within 48 hours. However, in 75% of these cases, the leaked key was not revoked, meaning that anyone who stole it during the exposure period could still use it later to mount attacks. Flare suggests that developers avoid storing secrets in container images, stop using static, long-lived credentials, and centralize their secrets management using a dedicated vault or secrets manager. Organizations should implement active scanning across the entire software development life cycle and revoke exposed secrets and invalidate old sessions immediately.

Our Certifications & Licenses

Industry-recognized certifications and quality standards

ISO/IEC 12785
ISO/IEC 5962 (SPDX)
ISO 9001:2015
ISO/IEC 19790